AJE Multisite Network Infrastructure
01
Overview
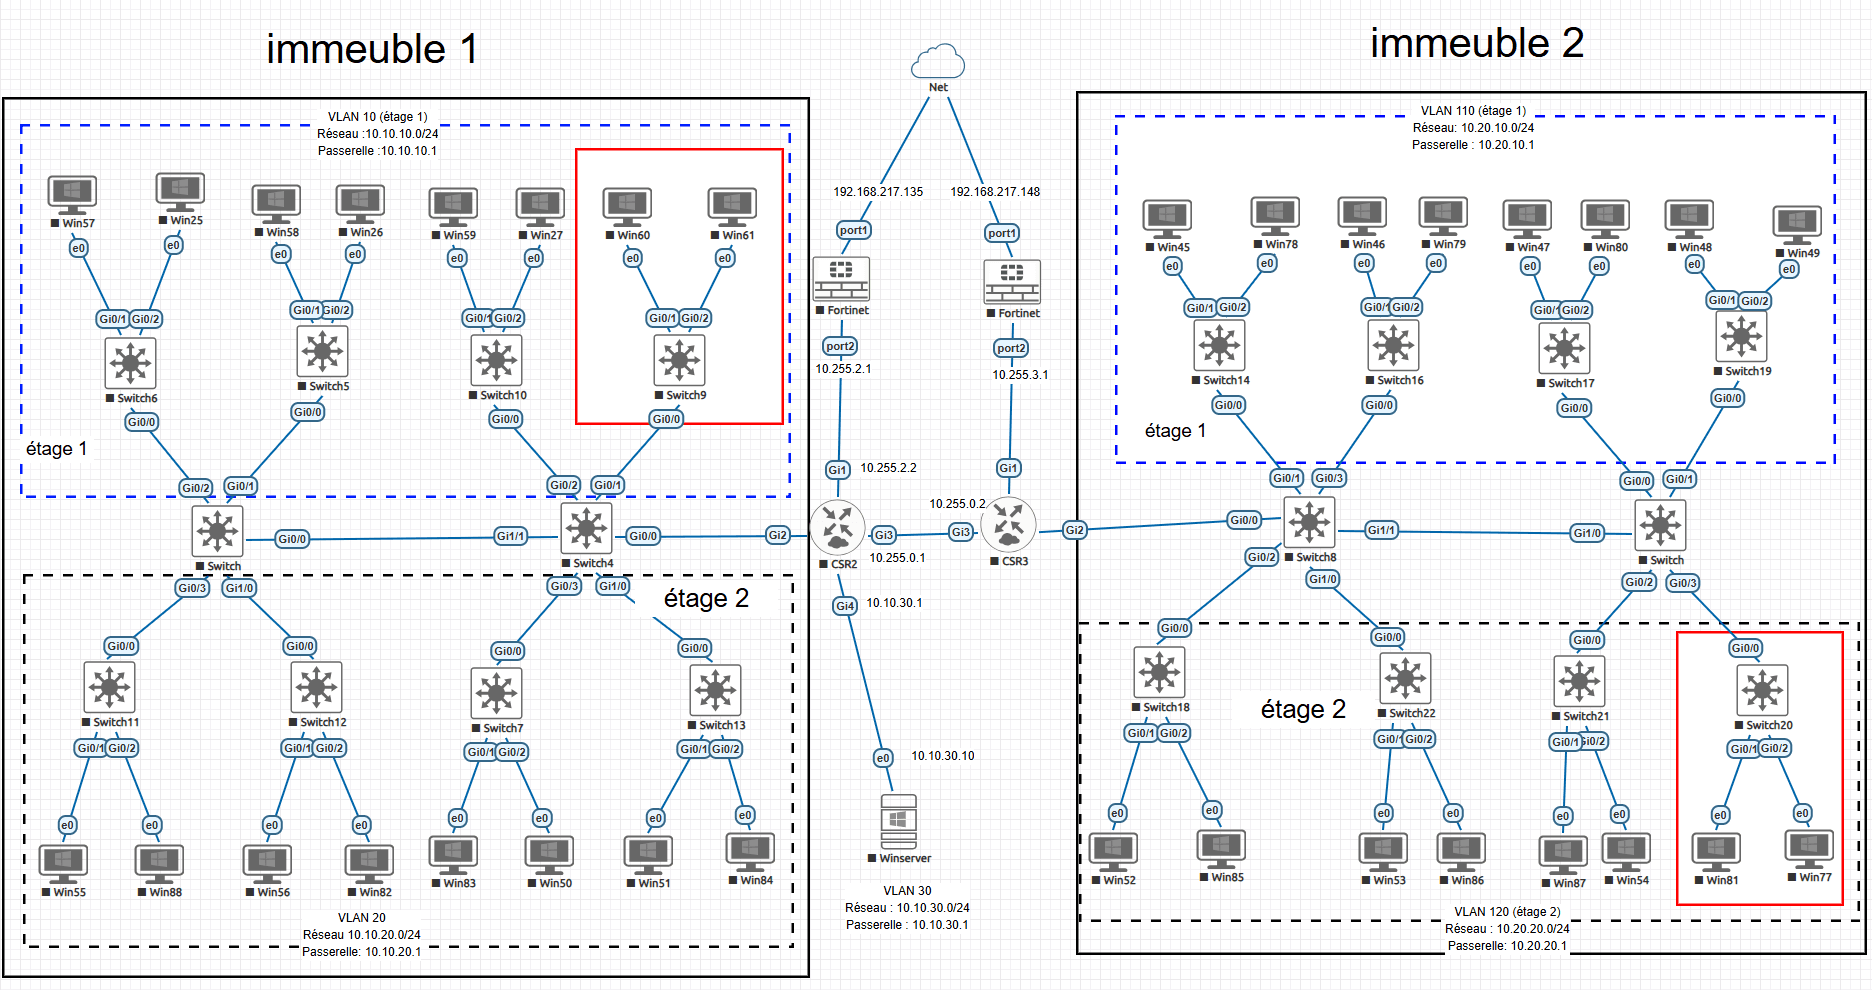
A simulated multisite network built to practice enterprise-grade design: several interconnected sites, each segmented internally and secured at the perimeter.
02
Problem
A flat, unsegmented network makes lateral movement easy and gives every device the same level of trust — the opposite of what a real multisite organization needs.
03
Solution
The network was split into VLANs by function, with inter-VLAN routing controlling what could talk to what, and FortiGate firewalls enforcing policy at each site boundary.
04
Architecture
Each site runs its own VLAN structure with dedicated switching and routing, interconnected through secured links and centralized firewall policy — all modeled and validated in EVE-NG before documentation.
05
Technologies
VLAN, inter-VLAN routing, switching, routing, FortiGate firewall policy, and EVE-NG for topology simulation.
06
Challenges
Getting inter-VLAN routing and firewall rules to agree with each other without accidentally blocking legitimate traffic took several iterations of testing and adjustment.
07
Result
A working, documented multisite topology with segmented traffic and enforced firewall policy — a reference lab for how a segmented enterprise network is actually built.
08