All projectsOpen to opportunities
CybersecuritySOC
Wazuh SOC
2025
01
Overview
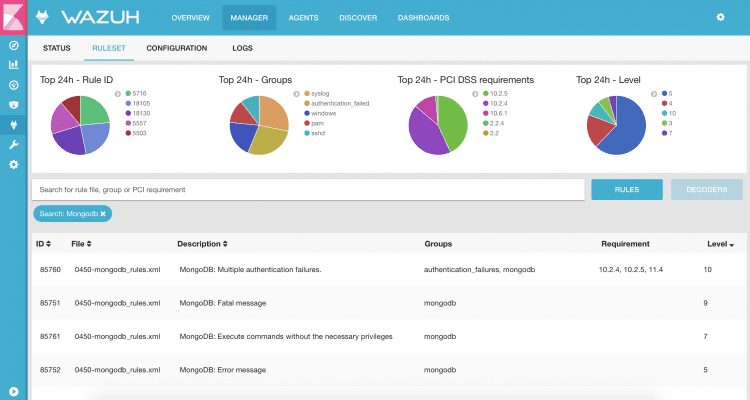
A Wazuh-based monitoring lab used to understand how a SOC actually watches and reacts to what's happening across an environment.
02
Problem
Without centralized logging and monitoring, security incidents are discovered too late, if at all.
03
Solution
Wazuh was deployed to collect and correlate logs from monitored endpoints, with alerting rules tuned to surface meaningful anomalies instead of noise.
05
Technologies
Wazuh (SIEM), log collection and correlation, alerting and detection rules.
06
Challenges
Tuning alert thresholds to catch real anomalies without drowning in false positives — a core SOC skill in itself.
07
Result
A functioning monitoring setup that gave hands-on experience with the detection and triage workflow a SOC analyst uses daily.
07
Technologies used
WazuhSIEMLog MonitoringThreat DetectionSecurity Analysis
Next projectCyberNight